Thursday, June 6, 2013

Get rid of System Doctor 2014 as a malicious impurity that claims to be security

System Doctor 2014 is a malicious impurity to your operating system that comes along misleading ads and other tricky installation schemes.
Features of the program do not provide for any activities related to proactive protection from, detection and extermination of computer threats. Therefore, the program is a 100% fraud.
Removal of System Doctor 2014 is a request by many users. They realize the alerts by the program are misleading, but cannot remove System Doctor 2014, for they do not gave a proper method.
In fact, the malware applies effort to prevent its extermination by blocking multiple processes and not allowing you to change system settings etc. To be able to delete the rogue while applying effort amounted basically to a few clicks from you, browse here to launch free scan. 


System Doctor 2014 activation codes (serial number, license key, unlock code):

AA39754E-715219CE
Activation is NOT ENOUGH to get rid of the System Doctor 2014 rogue. You might still have its records in Windows registry and receive annoying pop-ups. Learn how to Remove System Doctor 2014 malware manually.

Thursday, May 30, 2013

Get rid of Insecure.exe (Internet Security 2014) - unlock codes and free removal

Insecure.exe is a malicious process run by no less calamitous badware titled Internet Security 2014. Obviously, the process corresponds to same-name executable. In order to remove Insecure.exe, you need to ensure its relevant process is idle, otherwise system regulation will block the extermination.
Removal of Insecure.exe deletes critical executable and kills main process of Internet Security 2014, fake antispyware application that makes you stare at its intentional false positives from the very beginning of system session and on. Besides, it conflicts with useful apps and eventually paralyzes your OS so that you are strongly recommended clicking here (free scan link) in order to ensure extermination of the bad file and other components and associated leftovers of the counterfeited security suite above.

Internet Security 2014 activation codes (serial number, license key, unlock code):


Y68REW-T76FD1-U3VCF5A
Y86REW-T75FD5-U9VBF4A
Y76REW-T65FD5-U7VBF5A
Y86REW-T75FD5-9VB4A
SL55J-T54YHJ61-YHG88
Activation is NOT ENOUGH to get rid of the Internet Security 2014 rogue. You might still have its records in Windows registry and receive annoying pop-ups. Learn how to Remove Internet Security 2014 malware manually.

Tuesday, April 23, 2013

Remove XP Security Cleaner Pro fake antivirus as a it is dangerous to ignore it

XP Security Cleaner Pro is perhaps the most insecure resident to your operating system. A bundle of popups dressed up as virus related alerts and even full-featured scan conceals an aggressive kernel, which is a trojan of severely restrictive impact towards its host system, as well as adjacent local network environments.
Needless to say, the program provides a nice-looking illusion of memory scan for viruses being unable to identify a single parasite in the actuality, yet having not a slightest inclination to such activity either.
Removal of XP Security Cleaner Pro is not a procedure that one can complete by uninstalling, as that would do for a decent software product. Being a computer infection, the program just like a biological infection makes its best to survive within the host, so that it is good to run free scanner available here in order to get rid of XP Security Cleaner Pro for sure and for good, the suggested detection and extermination also encompasses real parasites.


XP Security Cleaner Pro activation code (serial number, license key):
9443-077673-5028
3425-814615-3990
2233-298080-3424
1147-175591-6550

Activation is NOT ENOUGH to get rid of the XP Security Cleaner Pro rogue. You might still have its records in Windows registry and receive annoying pop-ups. Use reliable anti-malware to get rid of this and other infections and fix virus problem.

Saturday, April 13, 2013

Removal of System Care Antivirus 3.7.32 to eliminate the fake that pretends to be Windows Security Center

System Care Antivirus 3.7.32 shows full set of fake alerts inherent to original Microsoft software aimed at protecting personal computers, from fake Windows Security Center to scan window featuring all imaginary threat names or, where names belong to real infections, no detection event has resulted into inclusion of such denominations into the scan results. Remove System Care Antivirus 3.7.32 as a misleading counterfeit that wants to bewilder users with popups wrapped into skins impersonating colors and graphics used in Microsoft software.
The malware is powered by trojan that makes intervention into any PC regardless of software environment it is based on. Where the environment is XP, the above interface is loaded. Naturally it is expected that a victim is a user of relevant OS. Exceptions, if happen, have not been reported to wide public.
Click here to get rid of System Care Antivirus 3.7.32 covering its entire kit of popups displaying mechanism and components responsible for blocking the system and other legit apps.


System Care Antivirus 3.7.32 activation code (serial number, license key):
AA39754E-715219CE

Activation is NOT ENOUGH to get rid of the System Care Antivirus 3.7.32 rogue. You might still have its records in Windows registry and receive annoying pop-ups. Use reliable anti-malware to get rid of this and other infections and fix virus problem.

Sunday, April 7, 2013

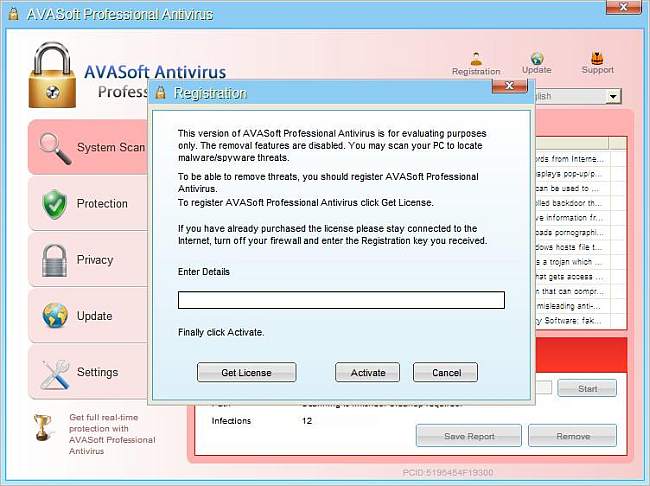
Get rid of AVASoft Antivirus Professional 3.7.30 the fraudulent reporter on imaginary threats

AVASoft Antivirus Professional 3.7.30 is not a remedy against viruses. The threats it reports are all fraud. True meaning of its messages for user is that the PC concerned is overtaken by dangerous counterfeit.
Apart from supplying deliberately misleading info, the rogue is responsible for denial of services attacks targeting, in particular, software for Internet navigation. It also has been observed to kill processes of random applications and commenting on resulted program failure claiming it is so-and-so threat it has detected induced the error.
Remove AVASoft Antivirus Professional 3.7.30 to get rid of misleading information and ensure legit programs run without interruptions caused by the malware attacks. Click here to complete the removal of this dangerous rogue and other infections reported by free scanner. 


AVASoft Antivirus Professional activation code (serial number, license key):
AA39754E-715219CE

Activation is NOT ENOUGH to get rid of the AVASoft Antivirus Professional 3.7.30 rogue. You might still have its records in Windows registry and receive annoying pop-ups. Use reliable anti-malware to get rid of this and other infections and fix virus problem.


Thursday, February 21, 2013

Remove "Twój Komputer Został Zablokowany" Virus and spare PLN 400

Twój Komputer Został Zablokowany Virus is vividly discussed in Polish (speaking) segment of the web. Plenty of observers have posted reports with titles suggesting that users whose PCs got victimized are to take it easy, for these are but the tricksters who stand behind.
True, the message the hackers post referring to the name of the Police that your PC has been blocked due to unauthorized cyber activity (nie sankcjonowanej aktywności cybernetycznej) is a fraud, and you must not pay PLN 400 in order to unlock your PC and avoid other legal consequences (Żeby odblokować komputer i unikanąć innych konsekwencji prawnych). However, the infection is not to be ignored. Failure to get rid of Twój Komputer Został Zablokowany Virus keeps your PC, in its major features, blocked by the rascals.
Click here to get timely and comprehensive help so that the removal of Twój Komputer Został Zablokowany Virus could be completed in full, with ultimate safety precaution and on free scan terms. 
Praca twojego komputera została zablokowana z powodu nie sankcjonowanej aktywności cybernetycznej.
Poniżej są wymienione możliwe naruszenia prawa:
Artykuł – 174. Prawo autorskie
Artykuł – 183. Pornografia […]
Artykuł 156. Rozsyłanie spamu o treści pornograficznej
Żeby odblokować computer i uníknąč innych konsekwencji prawnych, jesteś zobowiązany do zapłacenia grzywny w wysokości 400 PLN.


Monday, February 4, 2013

Remove Adware:Win32/PriceGong that stuns and burdens you with unrelated shopping alerts

Adware:Win32/PriceGong is an advertisement infection specific to 32 platforms utilizing Windows OS. It corresponds to the program, which denomination makes a part of the detection name. It is a malicious plug-in called Pricegong. The applet extends browser window with its toolbar and distorts appearance of many websites allegedly to make you familiar with best bids, “to suggest you a variety of attractive, alternative offers”.
Removal of Adware:Win32/PriceGong is recommended to eliminate unrelated ads that distract you and slows down browser, yet may block useful content of websites you are trying to reach. In order to get rid of Pricegong and other infections as detected by free scanner, do not hesistate clicking here.


Monday, January 28, 2013

Removal of Vista Security 2013 - free unlock codes

Vista Anti-Virus 2013 comes from websites that apply malicious Java scripts to drop a trojan that installs the program, which is but another insidious attempt of web-rascals to benefit on user’s blind trust to security software. Alas, there are much more fake security tools than genuine remedies to combat cyber pests.
The above routine does not make an exclusive method for the introduction of above program. Fake online scanners are applied to scare people into installing the infection with their own hands
To get rid of Vista Security 2013, special method or solution is to be applied. Free scanner available here enables you to remove Vista Security 2013 along with true threats detected in the course of its inspecting the memory of your PC.
It is critical to rid your PC of the above counterfeit, because, apart from burdening you with its silly popups, the malware does not let other applications run their processes pretending it has discovered viral impurity to their scripts.

screenshot from bleepingcomputer.com

 Vista Anti-Virus 2013 activation code (serial number, license key):

9443-077673-5028
3425-814615-3990
2233-298080-3424
1147-175591-6550


Activation is NOT ENOUGH to get rid of the Vista Anti-Virus 2013 rogue. You might still have its records in Windows registry and receive annoying pop-ups. Use reliable anti-malware to get rid of this and other infections and fix virus problem.

Saturday, January 5, 2013

Remove Meister Penalty Document, fake SOPA and PIPA message

Meister Penalty Document is another face for ransomware familiar to malware observers – another case of infamous UKASH, PaySafeCard, GreenDot MoneyPak virus. It is to be admitted that neither SOPA and PIPA mentioned in the popup as though they prosecute the user concerned, nor any of the above payment systems (UKASH etc.), actually support or stay behind the scan whatsoever. It is only their bad luck that hackers have selected their names to speak on their behalf and payment facilities to recommend as a money transferring solution, respectively. If it is your bad luck that your PC has got infected with the ransomware, stop it, but not in the way the misleading alert wants you: do not transfer any funds even if you suppose just to pay off, understanding the message is concocted by hackers. That will not do, for the ransomware, even if respond to the activation code entered, will not be gone for good. The only way to get rid of Meister Penalty Document completely is to detect and delete all its components.
Free scanner available here is a valid Meister Penalty Document removal tool plus a solution to rid your PC of its current threats and keep other infections off your working station.
Meister Penalty Document screenshot


Meister Penalty Document (Belgium UKASH virus) unlock code:
aes987156

Activation is NOT ENOUGH to get rid of the Meister Penalty Document (FCCU virus). You might still have its records in Windows registry and receive annoying pop-ups. Download reliable antimalware to get rid of this infection.

Friday, December 21, 2012

Remove Win7 Defender - license key and removal tool

Win7 Defender is prepared in hacker’s lab using template for popups with minimal changes made. To be precise, the changes are limited to introducing another name. That is, just a few days before the application under review, Win7Defender2013 had been released and displayed basically the same popups.
Therefore the removal of Win7 Defender is to be considered as extermination of Win7Defender2013 clone.
Just like its infamous predecessors, the malware has a bad habit of launching its own processes as user of affected PC orders any exe file to open. That often entails failure of the requested application to run while the unwanted one floods popups on the monitor. Launch free scan and get rid of Win7 Defender.


 Win7 Defender activation code (serial number, license key):

AA39754E-715219CE


Activation is NOT ENOUGH to get rid of the Win7 Defender rogue. You might still have its records in Windows registry and receive annoying pop-ups. Use reliable anti-malware to get rid of this and other infections and fix virus problem.

Thursday, December 20, 2012

Remove Trojan Horse Agent3.CPCF and prevent unauthorized, malicious contents

Trojan Horse Agent3.CPCF is a malicious object that infiltrates onto computer system due to user’s insecure habit of loading content. It is strongly recommended that you enhance your computer security in order to prevent this and similar infections from violating your right of choosing a content to be loaded onto your PC.
The point is that the infection comes along with another programs. Those might be legitimate and safe, but often simply missing, while the rogue is injected instead.
It is often dedicated to loading other parasites onto your PC. Therefore, removal of Trojan Horse Agent3.CPCF is not always a sufficient measure to ensue computer disinfection, at least to clean threats it drops on its own.
Click here to launch free scan and get rid of Trojan Horse Agent3.CPCF, as well as other parasites. The solution suggested, apart from aiding in the extermination, will prevent further installation of unauthorized, malicious contents.

Monday, November 26, 2012

Remove HTML/rce.gen3 to prevent malicious code execution

HTML/rce.gen3 marks a program that tries to compete a malicious payload, that is, to fulfill a task set by crooks. The method was first applied to successfully detect computer infection in 2007.
The program acts through browser vulnerabilities. A behavior based routine is used to identify the malware.
Removal of HTML/rce.gen3 is not limited to repair action related to a particular browser, for example, Internet Explorer. However, it might include it, and in the wild users often observe the detection as they are opening IE and reasonably conclude the detection is associated with that the software being opened.
Free scanner available here is a tool to get rid of HTML/rce.gen3 and other threats according to the detection report.

Monday, November 19, 2012

File Restore license key and unlock code for faster removal

File Restore is a misleading program. It is not a useful feature provided for Microsoft software environment.
Users either take a decision to install the program taking into account misleading information, for instance, online fake scanner for system errors, or get their computer infected with the rogue dropped as a trojan or worm.
Remove File Restore malware, as it fakes fixing of computer errors.
Click here to initiate free computer examination and get rid of File Restore malware as yet another example of software counterfeiting, a member of numerous malware strain.

 File Restore activation code (serial number, license key):

E-mail: mail@email.com
Activation Key:
08467206738602987934024759008355


Activation is NOT ENOUGH to get rid of the File Restore rogue. You might still have its records in Windows registry and receive annoying pop-ups. Learn how to Remove File Restore malware completely.

Thursday, November 15, 2012

Remove Trojan.Ransomlock.G as a piece of ransom claiming parasite

Trojan.Ransomlock.G is a technique to detect threats yet unknown to detecting facility. That is called a heuristic approach to threats identification. As you could have foreseen, false positives, wrong detections, abound, where the method is applied.
On the other hand, the detection often refers to critical threats, thus is certainly useful.
Removal of Trojan.Ransomlock.G is to target ransomware, malicious program that holds computers for ransom under various pretexts. That should not be misunderstood as though if there is no current attack of ransomware, the detection is a mistake, for it may refer to the malware leftovers or initial stages of malware invasion.
Click here to start free scan and get rid of Trojan.Ransomlock.G and other parasites detected heuristically or otherwise.

Tuesday, November 6, 2012

Remove Federal Computer Crime Unit Virus

Federal Computer Crime Unit Virus is incredibly efficient infection. According to the assessment of the authority which name stands for common reference to the virus (Belgium Police), approximately 1 of 8 users of compromised machines pay the so called fine demanded by hackers.
The scam goes as follows: a trojan is injected into computer using one of drive-by download routines available. The trojan blocks access to desktop and basic system features and shows popup containing the name of Belgium Police. The popup addresses users in French blaming on them visiting “le site qui contient la pornographie, la pornographie d’enfant, la sodomie et desactes de violence envers les enfants.”
It is critical that victims do not pay Euro 100 to hackers that they request in order to unlock PC and drop the charges. The payment methods they suggest are highly depersonalized. It would be quite difficult to get a refund upon filing a compliant to the Police and payment provider. However, Belgium Police still suggest a victim who has satisfied the financial demands of hackers to dispute chargers with payment provider.
Removal of Federal Computer Crime Unit Virus deals with ransomware powered by rootkit. It requires proficient assistance.
To get rid of Federal Computer Crime Unit Virus safely and efficiently, launch free scan routine with the tool available here.

Federal Computer Crime Unit Virus screenshot

Federal Computer Crime Unit Virus (Belgium UKASH virus) unlock code:
aes987156

Activation is NOT ENOUGH to get rid of the Federal Computer Crime Unit Virus (FCCU virus). You might still have its records in Windows registry and receive annoying pop-ups. Download reliable antimalware to get rid of this infection.

Monday, November 5, 2012

Remove Windows Protection Maintenance using valid unlock code and removal guide

Windows Protection Maintenance defends computer systems from weak antispyware. The program is a fake antivirus hostile toward genuine prosecutors of malware. If a true security tool is not efficiently protected either on the stage of installation or in its activities upon integration onto computer system, or both, it will not be able to complete Windows Protection Maintenance removal, for the rogue itself would remove the insufficiently armored tool or prevent it from installing.
Click here to launch free scanner and get rid of Windows Protection Maintenance so that the fraudulent application will no longer burden you with its popups that mimic scan menu, firewall alerts etc.
The rogue is a family malware. It has a number of related clones, with appearance nearly identical to its GUI. However, the method suggested above is unique, for the rogue contains a number of modifications as compared to any of its counterparts.


 Windows Protection Maintenance activation\unlock code (serial number, license key):

0W000-000B0-00T00-E0020


Activation is NOT ENOUGH to get rid of the Windows Protection Maintenance rogue. You might still have its records in Windows registry and receive annoying pop-ups. Learn how to Remove Windows Protection Maintenance malware completely.

Sunday, November 4, 2012

Remove Searchfunmoods.com hijacker that promotes it in a way inherent to misleading and illegal url

Searchfunmoods.com has a browser hijacker that ensures a stable flow of visitors to the url. This practice is common for promotion of a low quality, misleading, illegal online facility.
If your browser keeps opening the url in question under various conditions, especially if that restricts your access to other websites, removal of Searchfunmoods.com hijacker is needed. That is a matter of overall system cleanup. Do not waste time into attempts of resolving the issue by means of changing web-navigation software – the infection is beyond the limits of particular software.
Free scanner available here is a tool to get rid of Searchfunmoods.com along with other malicious residents on your PC.

Searchfunmoods.com screenshot:


Friday, November 2, 2012

Remove FBI Anti-Piracy Warning that fakes official Seal of the Bureau

FBI Anti-Piracy Warning virus is a fake message. There is a genuine alert, so called Federal Bureau of Investigation Seal, which a is a legal remedy as explained on US governmental website.
Naturally it has nothing to do with the fake, save that the fake attempts to benefit on user’s trust towards appeals made by officials. Removal of FBI Ant-Piracy Warning virus is strongly recommended, if you have got your PC locked, and see alert that pretends to be a notification on behalf of the Federal Bureau of Investigation.
To get rid of FBI Anti-Piracy Warning popup – start free scan followed by relevant extermination action.

FBI Anti-Piracy Warning virus screenshot

FBI Anti-Piracy Warning virus (French UKASH virus) unlock code:
aes987156

Activation is NOT ENOUGH to get rid of the FBI Anti-Piracy Warning virus (AICS virus). You might still have its records in Windows registry and receive annoying pop-ups. Download reliable antimalware to get rid of this infection.

Thursday, November 1, 2012

PC Defender Plus activation and removal procedure

PC Defender Plus is not limited to popups only. That somewhat justifies its name, for, unlike plain adware, it takes some action.
Alas, the action is only meant to block legit software, while not a single virus is prosecuted by the fake security program –and cannot be due to lack of relevant technical devices.
In the wild, the rogue has been observed to show a popup tiled Firewall Alert upon providing the name of counterfeit in question. Body of the alert says the main executable of current web-navigation program, for instance, ieplorer.exe, is infected with Trojan.JS.Fraud.ba (the name is random and may vary). On that background, the rogue may prevent users from accessing the web, as though to prevent passwords, account names exposure.
Remove PC Defender Plus targeting the malware in full. That is, PC Defender Plus removal is only complete, where both its files and registry entries are covered, because, for example, the registry values added as the rogue is installed may be responsible for a number of annoying web-redirects.
To get rid of the rogue antivirus as appropriate, initiate free scan with the tool available here.


 PC Defender Plus activation code (serial number, license key):

AA39754E-715219CE


Activation is NOT ENOUGH to get rid of the PC Defender Plus rogue. You might still have its records in Windows registry and receive annoying pop-ups. Learn how to Remove PC Defender Plus malware completely.

Monday, October 29, 2012

Remove W3i.IQ5.fraud and the malware it misleads users into loading

W3i.IQ5.fraud detection informs users of a misleading installer on their computer systems. It offers interface of a loader compatible with some freeware on exclusive terms. This is done to fool people into infecting their working stations with annoying adware by making them believe they are loading software of interest to them.
Removal of W3i.IQ5.fraud may target the adware loaded only, while the loader persists. In such a case, the misleading free installer may repeat the trick, so that the detection recurs until after you delete it (the downloader).
Get rid of W3i.IQ5.fraud in full: first of all, the suggested tool deletes the tricky installer, but then does not spare the content loaded through its interface.